Detect the threat behind the behavior.
Suspicious activity does not always look like an attack. vSOCBox UEBA helps security teams identify unusual behavior across users and entities, surface meaningful risk signals, and investigate activity with greater context.
- Behavioral anomaly detection
- Identity and entity risk context
- Investigation-ready signals
- Unified security visibility
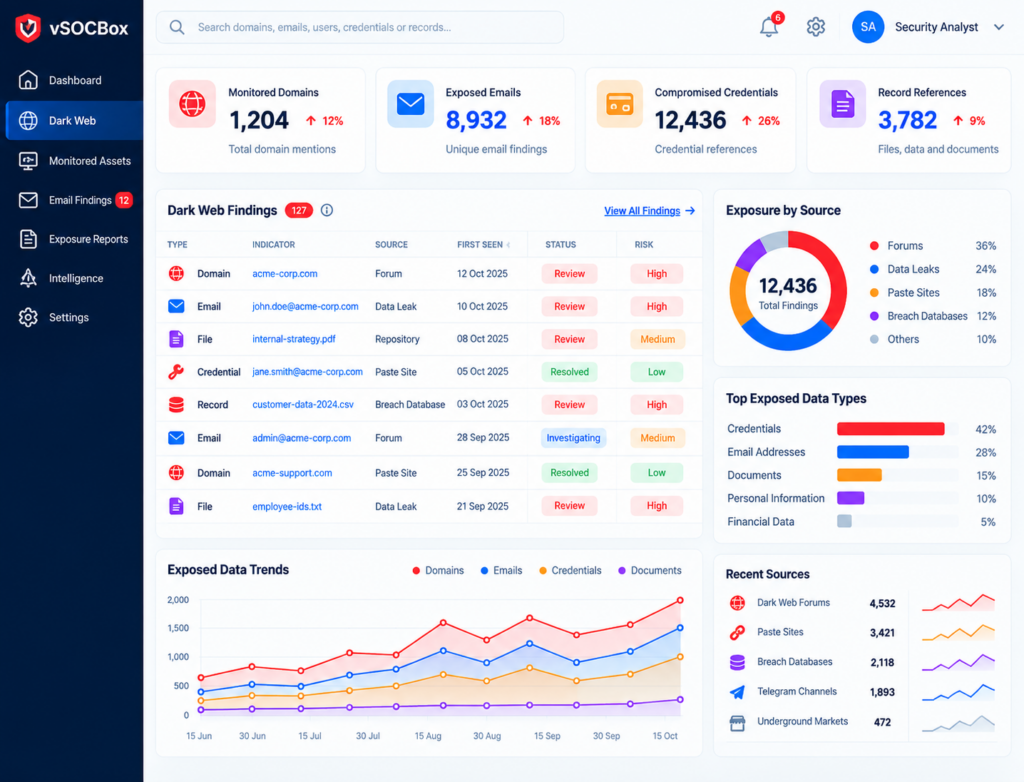
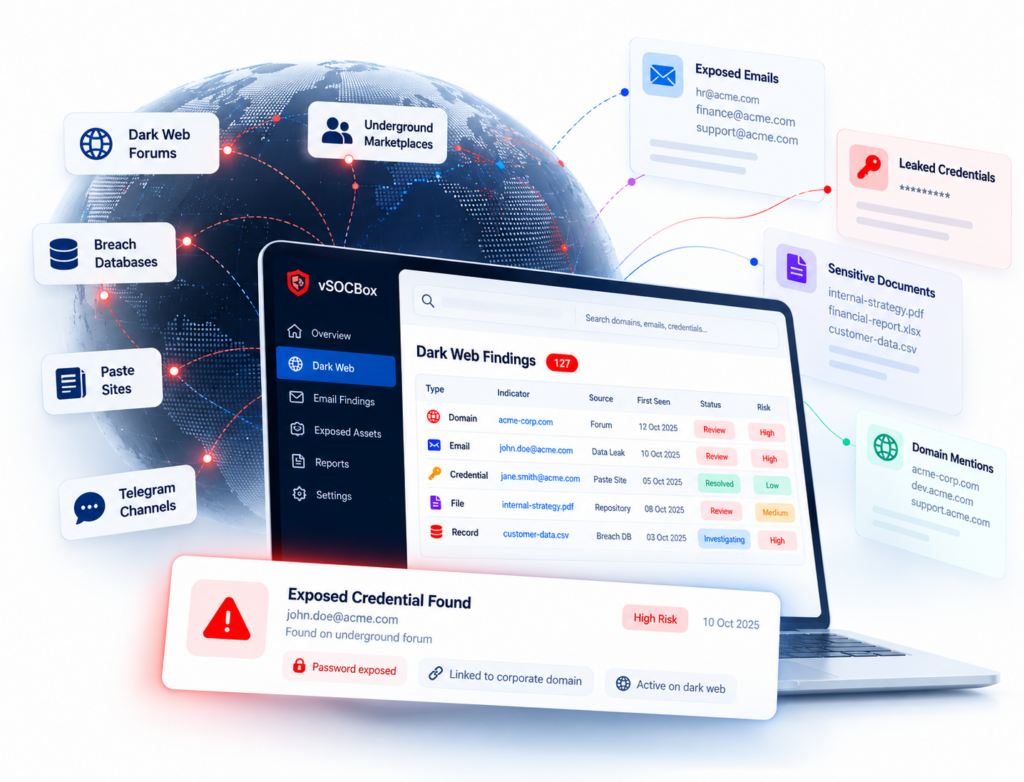
Find the unusual activity hiding in everyday operations.
Understand what changed—and why it may matter.
vSOCBox UEBA can help surface behavioral patterns that may indicate account compromise, insider risk, or unusual access when the relevant activity data is available.
Unusual access patterns
Highlight deviations in login times, locations, or resource access for review.
Identity and privilege risk
Surface suspicious account behavior, privilege changes, and potential misuse of authorized access.
Correlated security signals
Bring relevant events from connected tools together to support a more complete view of suspicious activity.
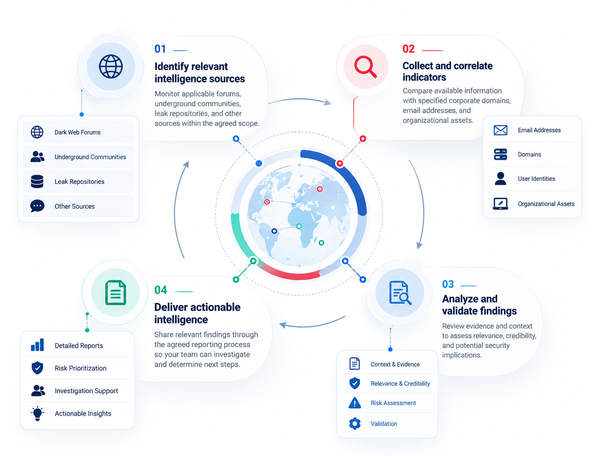
Connect the signals. Investigate with context. Respond with confidence.
-
Establish the context
Review the activity pattern and the entity associated with the anomaly.
-
Correlate related evidence
Examine connected identity, endpoint, network, or access events where integrations provide that data.
-
Prioritize the next action
Use available risk context to support triage, escalation, and configured response workflows.

Make behavioral risk visible across your enterprise.
-
For security leadership
Improve visibility into identity-related risk and investigation priorities.
-
For SOC teams
Add behavioral context to alert triage and incident investigation.
-
For IT and identity teams
Investigate unusual access and potentially risky account behavior.
-
For complex environments
Support a broader view across distributed users, assets, and connected systems.
Protect Your Enterprise with vSOCBox
Secure your organization from advanced threats with vSOCBoxTM, a powerful SIEM and UEBA solution. Gain unparalleled visibility, detect anomalies, and respond swiftly to incidents.
TRUSTED BY LEADING ORGANIZATION